
About CyberMoat
CyberMoat applies security thinking to capital allocation.
Threat modelling, attack surfaces, incentives, failure modes — the habits of mind that locate structural weakness in a complex system before it becomes catastrophic. Markets are complex systems. They fail structurally, and for recognisable reasons: misaligned incentives, assumptions nobody stress-tested, narratives that outrun the economics underneath them.
Who writes this
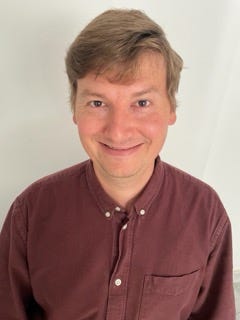
Michał Rzepka. For more than fifteen years I have worked in cybersecurity — penetration testing, application security and red teaming, mostly inside banking and financial infrastructure. That work turns on a single question: what does this system actually do, as opposed to what the people who own it believe it does?
CyberMoat asks the same question about businesses and the prices attached to them.
The technical background is not decoration, but it is not universal either. It is a genuine edge in a narrow set of places — software economics, cybersecurity, fintech and payment infrastructure, cloud architecture, and anywhere a company’s technical claims are hard for a generalist analyst to evaluate. Where it isn’t an edge, I don’t pretend it is.
What you’ll find here
Company research, concentrated where technical understanding changes the conclusion:
Moat analysis — and specifically whether technological change is strengthening a moat or quietly commoditising it
Software and SaaS economics in an era of collapsing development costs
Fintech, digital banking and payment infrastructure, with particular attention to Korea
The European space supply chain, including the less obvious suppliers
Polish small and micro caps on GPW and NewConnect, including companies nobody else covers
Macro, when it changes how a business should be valued
Every piece is trying to answer the same question: what does the market currently believe, where might that be wrong, and is the gap large enough to matter?
This is not a high-frequency newsletter. I publish when there is something worth examining properly.
How I work
Facts, management claims, inference and hypothesis are labelled as what they are, and a hypothesis never quietly becomes a fact. Primary sources come first — filings, annual and interim reports, investor presentations, earnings calls, regulatory statistics. Ratios get recalculated rather than copied from a screener. The strongest bear case gets stated explicitly, including against positions I hold.
For small and obscure companies, governance gets the same scrutiny as the operating business: shareholder structure, related parties, management history, dilution, capital raises, changes of control.
Where the evidence doesn’t support a conclusion, the piece says so.
What this is not
CyberMoat is not investment advice and is not a recommendation service. I am a cybersecurity professional who researches companies — not a licensed investment adviser — and nothing published here is intended as, or should be relied upon as, personalised investment advice. Positions may be held in securities discussed, and where they are, they are disclosed.
Do your own work. That is rather the point.
Who it’s for
People responsible for capital who take that responsibility seriously: allocators, operators, founders, family offices, and anyone who would rather read one careful argument than ten confident ones.
Working together
Alongside CyberMoat I run Arcana Security, a boutique security consultancy. For investors, that means technology and cybersecurity due diligence: architecture and security review, assessment of a target’s technical claims, and competitive or sector mapping in technical markets — the work of establishing whether an engineering story survives contact with the engineering.
If that would be useful: michal@cybermoat.net.
— Michał Rzepka
Detecting anomalies. Securing opportunities.
